Are your PBN's SSL certificates creating a public roadmap for Google to de-index your entire network? For years, securing a website with SSL was a straightforward best practice. Now, a system designed for security could be the very thing that exposes your private blog network.
Understanding PBN SSL Certificate Transparency: Risks and Best Practices is crucial for anyone operating a network in 2026. Certificate Transparency (CT) logs are public, immutable records of every SSL certificate issued. While intended to improve web security, these logs can inadvertently create a clear footprint, linking all your PBN domains together and potentially to your money sites, making them an easy target for de-indexing by search engines.
What Is Certificate Transparency and Why It Matters for PBNs
Certificate Transparency (CT) is an open framework and public logging system that records all issued SSL/TLS certificates. Its primary goal is to allow domain owners, certificate authorities, and web users to audit and monitor certificate issuance, helping to detect mistakenly or maliciously issued certificates. When a Certificate Authority (CA) issues an SSL certificate for a domain, it must submit that certificate to at least two public Certificate Transparency logs.
For PBN owners, this system presents a significant operational risk. Every certificate you acquire for your PBN domains is permanently recorded in these publicly accessible databases. Anyone, including Google and your competitors, can query these logs to see which certificates have been issued for any domain. This information, when analyzed in aggregate, can reveal patterns that you have worked hard to conceal, effectively undermining your network's privacy and security.
The implications are profound. What was once a private transaction between you and a certificate provider is now a public declaration. If not managed carefully, these public records can connect the dots between your otherwise disconnected PBN assets. For anyone serious about maintaining a long-term, effective PBN strategy, understanding and navigating CT logs is no longer optional; it's a fundamental aspect of network security. A well-managed network requires careful planning, which can be compared to the detailed strategies found in a PBNs vs guest posts vs niche edits guide.
The Hidden Risks: How CT Logs Can Expose Your PBN Footprint
The danger of CT logs lies in the data trails they create. While a single certificate entry might seem harmless, the accumulation of these entries across your network can paint a detailed picture for anyone who knows where to look. These logs provide concrete data points that can be used to link domains far more reliably than traditional footprint analysis methods like IP addresses or WHOIS data, which can often be obscured.
Revealing Your Entire Network Through a Single Certificate
The most direct way CT logs can expose you is through the use of multi-domain or wildcard SSL certificates. If you use a single certificate to cover multiple PBN domains, all of those domain names are explicitly listed within the certificate's details. This information is then published in the CT log, creating an undeniable, public list of domains that are under your control. It's the equivalent of handing Google a blueprint of your network.
Even if you use separate certificates, a pattern can still emerge. For instance, if you purchase and install certificates for ten different PBN domains from the same Certificate Authority on the same day, that simultaneous activity creates a strong association. Sophisticated analysis can easily flag these domains as being related, even without a direct link in a single certificate. This batch processing is a common mistake that prioritizes convenience over security, leaving a significant footprint.
Linking PBN Domains to Your Money Sites
One of the gravest errors is creating an association between your PBN and your primary money sites. This can happen if you use the same contact email address, organization name, or even the same hosting account to manage SSL certificates for both your PBN domains and your legitimate business websites. When this information is recorded in the CT log, it creates a direct, verifiable link that search engines can use to penalize your money site.
This risk extends beyond direct information matching. If your money site and PBN domains all use certificates from the same niche provider or are all renewed within the same week, it forms a behavioral link. Algorithms are designed to detect such anomalies. The goal of a PBN is to appear as a collection of independent, authoritative sites; linking them to your money site via SSL data completely defeats this purpose and puts your main asset at risk. buy niche edits safely.
"In 2026, ignoring PBN SSL certificate transparency is like leaving the front door of your house wide open. The data in CT logs is permanent and public, providing a treasure trove of information for anyone looking to uncover network footprints. Proper SSL management is no longer a suggestion; it's a critical component of operational security."
Creating Identifiable Ownership Patterns for Google
Google's ability to recognize patterns far exceeds manual analysis. CT logs provide a clean, structured dataset to feed into its algorithms. Consistent use of the same Certificate Authority, such as relying exclusively on free Let's Encrypt certificates or only using Cloudflare issued certificates, creates a strong and easily identifiable pattern across your network. Similarly, renewing all your certificates in the same month each year is another red flag.
These patterns extend to the technical details of the certificates themselves. Using the same encryption algorithms, key lengths, or validation methods across dozens of domains suggests a single controlling entity. To remain undetected, your PBN's SSL portfolio must look as random and diverse as the internet itself. Every point of consistency is another piece of the puzzle that can be used to identify and devalue your entire network. This is why many SEO professionals now explore different link-building tactics, comparing the value of niche edits vs guest posts as alternatives or supplements to PBNs.
Best Practices for PBN SSL Management in 2026
Given the risks, adopting a proactive and strategic approach to SSL management is essential for the longevity of any PBN. The goal is to create diversity and avoid predictable patterns that can be easily flagged by automated systems. The following practices are critical for anyone operating a PBN in the current landscape.
Diversify Your Certificate Authorities
Do not rely on a single Certificate Authority (CA) for all your domains. Using only free certificates from Let's Encrypt or only the default certificates from a specific host is a massive footprint. Instead, create a diverse portfolio of SSL providers. Mix and match between popular free and paid options to mimic a natural ownership profile.
Your list of CAs should include a variety of providers, such as:
- Let's Encrypt (Free)
- Sectigo (formerly Comodo) (Paid)
- DigiCert (Paid)
- GoDaddy (Paid)
- ZeroSSL (Free/Paid)
Avoid Using Wildcard SSL Certificates
Wildcard SSL certificates, which cover a domain and all its subdomains (e.g., *.yourpbndomain.com), are a major red flag for PBNs. They are designed for legitimate businesses with complex web infrastructures, not for single-page blogs. Using one instantly links all associated subdomains together and signals an unnatural setup for a supposed standalone site. high DR backlinks.
Furthermore, the wildcard entry itself is a clear indicator in CT logs. It publicly states that you intended to secure multiple sub-hosts under a single entity. For PBN purposes, always opt for single-domain certificates. While it requires more management effort to secure each domain or subdomain individually, the security benefits of avoiding this obvious footprint are well worth it.
Stagger Certificate Issuance and Renewal Dates
Registering or renewing SSL certificates for all your PBN domains within the same day or week is one of the most common and easily detectable mistakes. This batch processing creates a timestamp pattern that is simple to identify in CT logs. A natural collection of websites would have certificates that expire and are renewed at random times throughout the year.
To combat this, create a schedule to stagger the issuance and renewal of your certificates. If you acquire a batch of new domains, do not secure them all at once. Spread the SSL setup over several weeks or even months. Use a calendar or project management tool to track renewal dates and ensure they are distributed randomly across the year. This simple practice dramatically increases the apparent randomness of your network.
Use Different Domain Registration Information
The information used to register your domain (WHOIS data) and the information used to validate your SSL certificate should be diversified. While many PBN owners use WHOIS privacy, the details submitted to the CA during the validation process can still create a link. Avoid using the same administrator email, technical contact, or organization name across your PBN domains.
For domain validation (DV) certificates, the process is often automated, but for organization validation (OV) or extended validation (EV) certificates (which should generally be avoided for PBNs), the details are more scrutinized and logged. Stick to DV certificates and ensure you are using unique email addresses for each one. This level of detail management is what separates a resilient, long-lasting network from one that is easily dismantled. This is especially true for high-stakes industries where services like finance PBN links require utmost discretion.
| Aspect | Bad Practice (High Risk) | Good Practice (Low Risk) |
|---|---|---|
| Certificate Authority | Using only one provider (e.g., Let's Encrypt) for all domains. | Diversifying across multiple CAs (e.g., Let's Encrypt, Sectigo, DigiCert). |
| Certificate Type | Using wildcard or multi-domain certificates. | Using single-domain certificates for each site. |
| Issuance/Renewal | Registering or renewing all certificates in the same week. | Staggering issuance and renewal dates randomly throughout the year. |
| Contact Information | Using the same email or contact details for all certificates. | Using unique contact information and emails for each domain. |
| Monitoring | Ignoring CT logs and assuming SSL is 'set and forget'. | Actively performing SSL monitoring and using CT log search tools. |
How to Monitor Certificate Transparency Logs for Your Domains
Passive avoidance of footprints is only half the battle. Active monitoring is essential to ensure no unauthorized certificates are issued for your domains and to keep an eye on your own public footprint. Fortunately, several tools and services are available to help you monitor certificate transparency logs effectively.
Using Free Online CT Log Search Tools
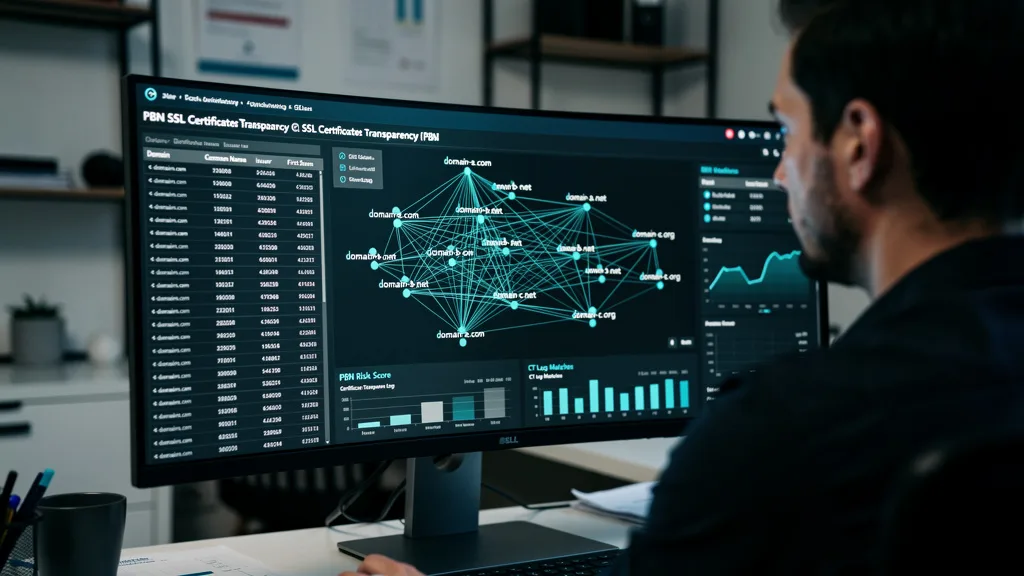
Several free online tools allow you to search CT logs for any domain name. The most popular is crt.sh, which provides a comprehensive search of multiple logs. To use it, you simply enter a domain name, and it will return a list of all certificates ever issued for that domain, including details about the issuer, issuance date, and expiration date.
Other major tech companies also provide their own search tools. Regularly using these tools to check your PBN domains allows you to verify that your diversification strategies are working and that no unexpected associations are being created. It's a quick, manual way to audit your network's public SSL profile. This proactive check is a core part of managing powerful assets like high authority PBN backlinks.
Setting Up Automated Monitoring and Alerts
For those managing a larger network, manual checks can become tedious and impractical. This is where automated certificate transparency monitoring services come in. These services continuously scan CT logs and send you an alert via email or another notification method the moment a new certificate is issued for a domain you are monitoring.
This automation provides an invaluable `early warning` system. It not only helps you track your own certificate issuances but also protects you against phishing attacks or mis-issued certificates by third parties. Services like those offered by Cloudflare or other specialized security companies can be configured to watch your entire domain portfolio. As Certificate transparency logs can expose internal projects, setting up an alert is a crucial defensive measure for any serious webmaster.
Key Takeaways
- Certificate Transparency is Public: All SSL/TLS certificates are recorded in public, immutable logs that anyone, including Google, can search.
- CT Logs Create Footprints: These logs can reveal connections between your PBN domains through shared certificate authorities, issuance dates, and contact information.
- Diversification is Key: To avoid detection, you must diversify your Certificate Authorities, stagger issuance and renewal dates, and use unique information for each domain.
- Avoid Obvious Red Flags: Never use wildcard or multi-domain SSL certificates for PBNs, as they explicitly link your assets together.
- Active Monitoring is Non-Negotiable: Regularly use free CT log search tools or set up automated alerts to monitor your domains for new certificate issuances and maintain network security.
Frequently Asked Questions
Does using Cloudflare for a PBN hide it from CT logs?
No, using Cloudflare does not hide your domain from Certificate Transparency logs. When Cloudflare issues an SSL certificate for your site, whether it's their Universal SSL or a dedicated certificate, that certificate is still submitted to public CT logs. The entry will list Cloudflare as the issuer.
While Cloudflare offers many security and performance benefits, relying on it for all your PBN domains creates a significant footprint. A network where every domain resolves through Cloudflare and uses a Cloudflare-issued certificate is easy to identify. It's better to use Cloudflare on some domains but mix it with other hosting and CDN providers to maintain diversity.
Are free SSL certificates like Let's Encrypt bad for PBNs?
Free SSL certificates like Let's Encrypt are not inherently bad for PBNs, but over-reliance on them is. Let's Encrypt is the most popular CA in the world, so using it for some of your domains is perfectly natural. The problem arises when 100% of your PBN domains use Let's Encrypt.
This uniformity creates a pattern that suggests a single owner managing all the sites with a cost-saving motive. A healthy, natural-looking PBN portfolio should include a mix of certificates from different providers, including both free and paid options. This diversification makes the network appear more organic and less like a centrally managed operation.
Can I remove my domain from a public Certificate Transparency log?
No, you cannot remove a domain or a certificate entry from a public Certificate Transparency log. The logs are designed to be append-only, tamper-proof, and permanent. This immutability is a core feature of the CT framework, as it ensures a complete and auditable history of all certificates that have been issued.
Once a certificate is issued and logged, that record exists forever. This is why it is so critical to get your SSL strategy right from the beginning. There are no take-backs or deletions. Your only course of action is to manage future issuances carefully and, if a major mistake was made, consider abandoning the compromised domain.
What is the biggest SSL mistake PBN owners make in 2026?
The single biggest SSL mistake PBN owners make in 2026 is ignorance: specifically, ignoring the existence and implications of Certificate Transparency logs. Many still treat SSL as a simple 'set it and forget it' task, focusing only on getting the green padlock in the browser without considering the public data trail they are creating.
This ignorance leads to all the classic errors: using the same CA for every domain, renewing all certificates at once, and using wildcard certificates for convenience. These actions, driven by a lack of awareness about CT logs, create easily detectable footprints that put the entire network at risk. Proactive, informed SSL management is the biggest differentiator for a successful PBN today.
How often should I check CT logs for my PBN domains?
The ideal frequency for checking CT logs depends on the size and activity of your network. For maximum security, setting up automated monitoring is the best practice. This ensures you receive real-time alerts the moment any new certificate is issued for your domains, whether by you or an unauthorized party.
If you prefer manual checks, a good rule of thumb is to check at least once per quarter. Additionally, you should always perform a check immediately after setting up a new domain and installing its SSL certificate to verify how it appears in the public logs. Regular audits help you stay on top of your public footprint and catch potential issues before they escalate.
Conclusion
In 2026, managing a PBN requires a level of operational security that goes far beyond hiding IP addresses and WHOIS data. PBN SSL Certificate Transparency has turned a standard security measure into a potential liability. The key takeaway is that every SSL certificate you issue is a public statement, and these statements, when viewed together, tell a story about your network. By diversifying your certificate authorities, staggering renewals, avoiding obvious red flags like wildcard certificates, and actively monitoring CT logs, you can control that narrative and protect your valuable assets from de-indexing. This proactive approach is no longer optional; it is the foundation of a resilient and effective PBN strategy.
Ready to build a powerful and secure link-building foundation without the headaches? Our team understands the nuances of network security and can help you develop a strategy that delivers results safely. Let's discuss how we can help you achieve your SEO goals. Get a Link Plan today.